
Best in Class SBOM Management
Generate, manage, and share accurate Software Bills of Materials (SBOMs) to meet regulatory requirements and enhance supply chain security.
Regulatory coverage
One platform for SBOM compliance
FOSSA helps you generate, manage, and share SBOMs that align with the frameworks regulators and customers ask for.
- CRAEU Cyber Resilience Act
- FDAMedical device guidance
- PCI DSSPayment card standard
- DORAEU digital resilience
- NTIAMinimum SBOM elements
- SEBIIndia securities rules
FOSSA addresses SBOM requirements across these frameworks and more.
Complete SBOM Lifecycle Management
FOSSA gives organizations the tools you need to manage every part of the SBOM lifecycle, from creation to distribution.
Generate accurate and precise SBOMs with a complete report of all code dependencies up to unlimited depth. Create SBOMs for any prior version of your software.
Import SBOMs in industry-standard formats to understand and control license and security risks in your third-party software dependencies.
Choose from multiple formats, including CycloneDX and SPDX. Use FOSSA to securely share your SBOM with customers and regulators.
Keep your SBOMs current with FOSSA's auto-update feature. Manage all SBOMs, including ones from third parties, in one centralized place.
SBOM Use Cases
Discover how FOSSA's comprehensive SBOM solution addresses multiple business needs across your organization.
Regulatory Compliance
Comply with global cybersecurity regulations that require organizations to produce machine-readable SBOMs with each product. FOSSA supports generating and ingesting SBOMs for all major formats.
- ✓Easily customizable configurations to modify SBOM reports
- ✓Comprehensive SPDX and CycloneDX support (generation and import)
- ✓Automated VEX attestations
- ✓Historic tracking across SBOM versions
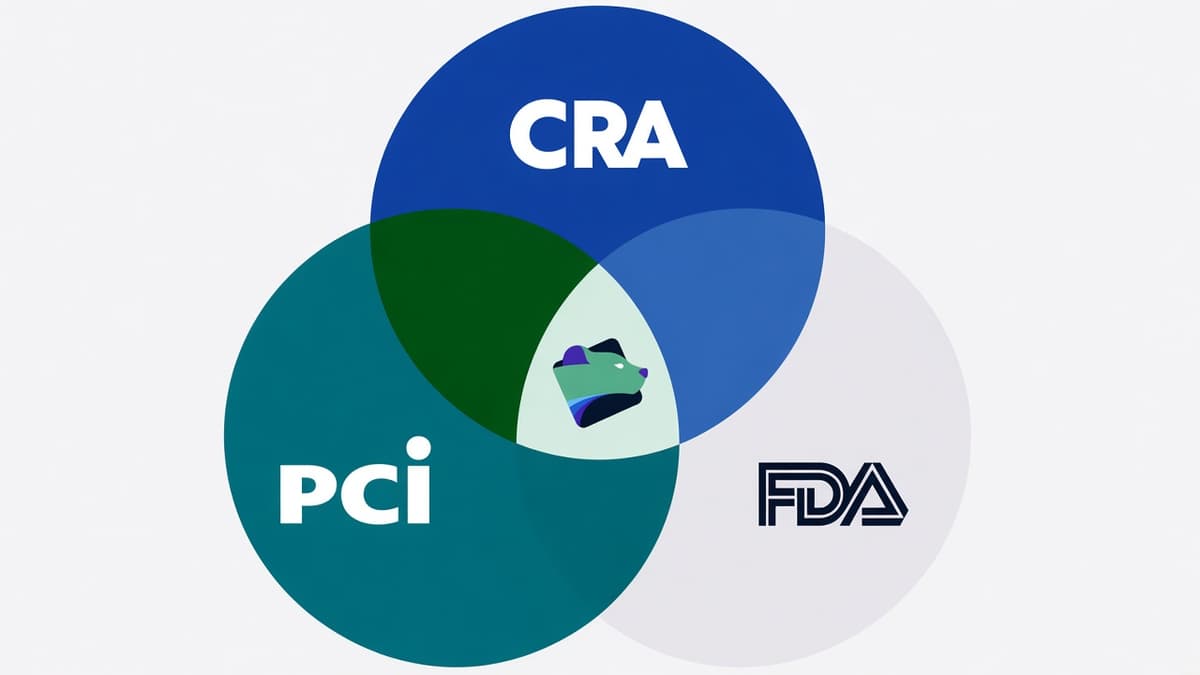
Meeting Global SBOM Requirements
Regulatory bodies across the world have implemented SBOM requirements. FOSSA's scanning and reporting platform significantly simplifies the compliance process.
Due Diligence
Simplify pre-IPO, M&A, and fundraising due diligence with audit-grade reports that can be generated in just a few clicks. Avoid surprises with comprehensive, accurate SBOMs and compliance reports that are updated in real-time.
- ✓M&A transaction readiness
- ✓Investor security review preparation
- ✓Acquisition integration planning
- ✓IP audits and risk assessments
Reduce Due Diligence Time by 90%
FOSSA SBOMs provide a complete inventory of your software components, making due diligence processes faster and more thorough for quicker transaction closings.
Customer Requests
Easily customize your SBOM to meet a wide range of customer requests. Use FOSSA's SBOM hosting service for easy customer access, or download and distribute a copy yourself.
- ✓Custom SBOM formats and content
- ✓Hosted SBOM portals for easy access
- ✓Version-specific SBOMs for products
- ✓Access controls and authentication
Product SBOM Portal
Securely share SBOMs with your customers
FOSSA's SBOM Portal allows you to easily share compliance information with customers while maintaining control over access and versioning.
Supply Chain Security
Stay on top of and address vulnerabilities impacting your applications. Import and analyze third-party SBOMs to understand and manage supply chain risk across your ecosystem.
- ✓SBOM-based vulnerability monitoring
- ✓Third-party SBOM analysis
- ✓Supply chain risk assessment
- ✓Component provenance tracking
Detected in component: log4j-core@2.14.1
Detected in component: axios@0.21.1
License Compliance
Detect and inventory the open source licenses in your application. Fulfill attribution notice requirements with FOSSA's compliance reports to ensure legal compliance.
- ✓License identification and tracking
- ✓Attribution notice generation
- ✓License obligation management
- ✓Policy enforcement and alerts
License Distribution
What is an SBOM?
A Software Bill of Materials (SBOM) is a formal, machine-readable inventory of software components, libraries, and dependencies used in an application. It’s becoming increasingly essential for compliance with global cybersecurity regulations, including the [EU Cyber Resilience Act (CRA)](https://fossa.com/learn/cyber-resilience-act/) and the [requirements from the U.S. FDA](https://fossa.com/blog/sbom-requirements-fda-cybersecurity-supply-chain-security/).
Complete Inventory
A comprehensive list of all components, including direct and transitive dependencies in your software.
Enhanced Security
Quickly identify affected components when new vulnerabilities are discovered.
Standardized Format
Machine-readable formats like CycloneDX and SPDX enable automation and interoperability.
Comprehensive SBOM Solution
FOSSA’s SBOM management platform provides everything you need to generate, validate, manage, and share Software Bills of Materials across your organization.
Accurate Generation
Create precise SBOMs that include all direct and transitive dependencies across multiple package managers.
Multiple Formats
Export SBOMs in CycloneDX, SPDX, and other formats to meet different regulatory and customer requirements.
Centralized Repository
Store and version all your SBOMs in a secure, searchable repository with access controls.
CI/CD Integration
Automatically generate and validate SBOMs as part of your DevOps pipeline, with GitHub and GitLab integrations.
Security Insights
Enrich SBOMs with vulnerability data to quickly identify and remediate security issues.
Secure Sharing
Easily share SBOMs with customers, partners, and regulators with controlled access permissions.